" height="101px" id="nbwo4Zi91" width="372.00001062700176px"/></svg>)
Credential Phishing
Frame.io Phishing Hides an AiTM Microsoft 365 Login Inside a Shared PDF
3 min read
Threat snapshot
Attack Type
Credential Phishing
Attack Vector
Trusted Platform Abuse
Attack Goal
Credential Theft
Impersonated Brand
Microsoft 365
Published
At a glance
Sender: Frame.io’s own notification system
Volume: 22 emails to one enterprise tenant in two hours on Aug 27, 2026
Payload: a PDF preview with no clickable link; the real link was a /URI annotation inside the file
Target: Microsoft 365 credentials via an adversary-in-the-middle (AiTM) login clone
What happened
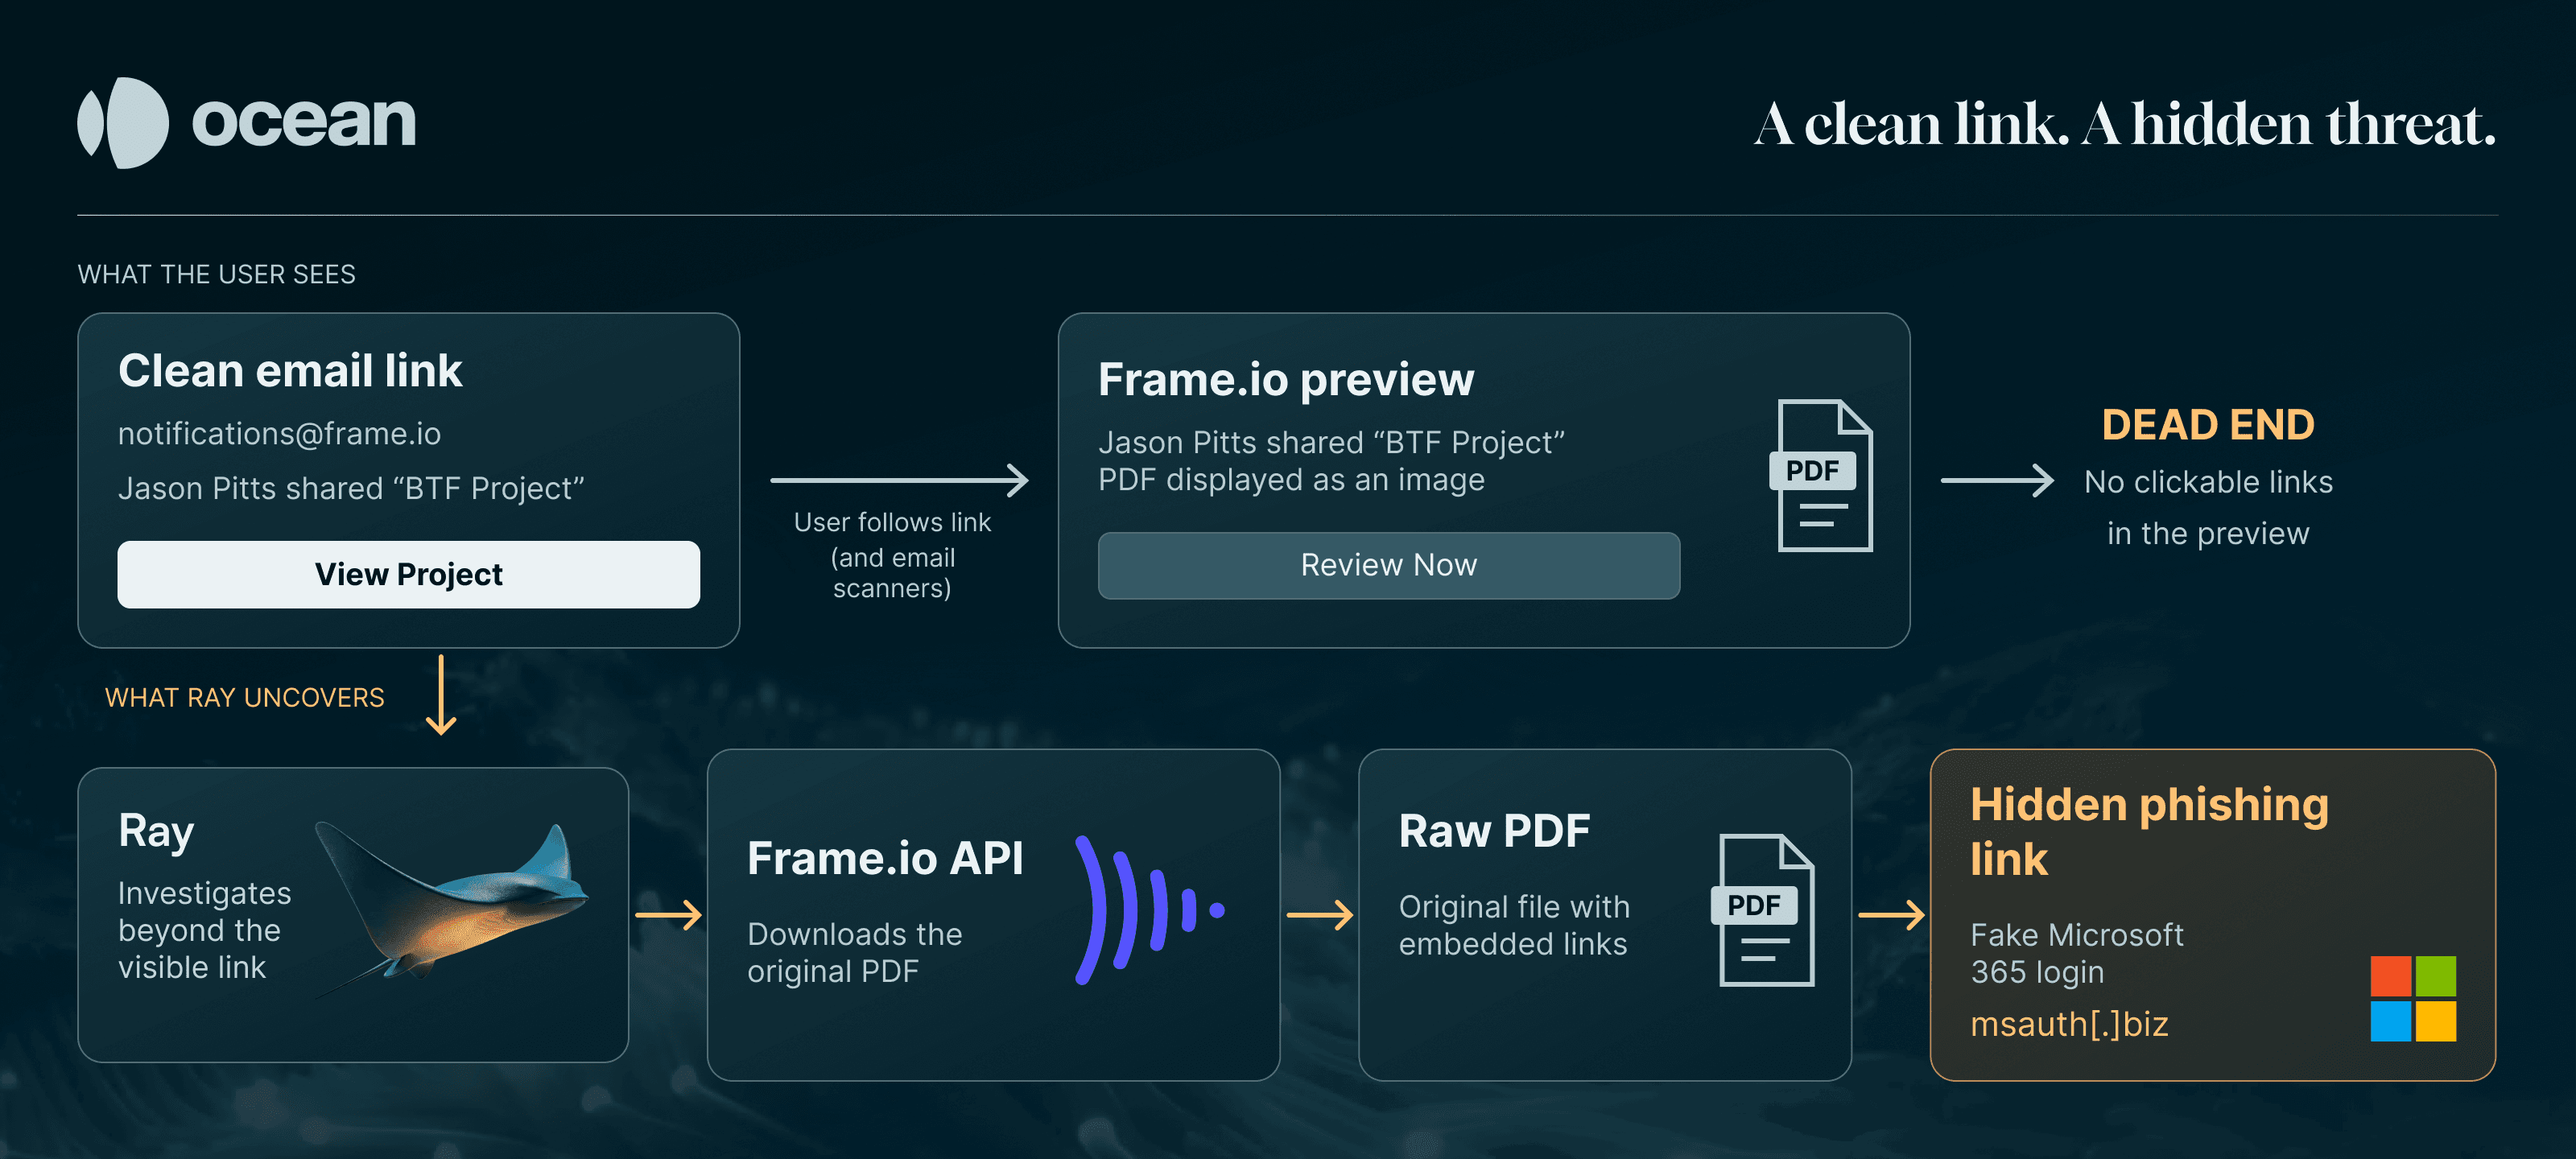
Employees received “Jason Pitts shared “BTF Project” with you” from Frame.io’s real notification system, so the emails passed gateway checks. The share link pointed to Frame.io, and the shared PDF rendered as a non-clickable preview. The malicious link was hidden inside the file.
How the redirect chain worked
Frame.io notification email
Frame.io share link
A pages.dev redirector referenced inside the PDF
A 301 redirect to a newly registered domain, msauth[.]biz, behind a Cloudflare Turnstile CAPTCHA
Obfuscated JavaScript serving a Microsoft 365 login clone
Why it got past email security
What the filter checks | What this email did |
|---|---|
Sender authentication | Passed. Sent from Frame.io’s own servers |
First-hop link | A legitimate Frame.io share URL |
Attachment scanning | No attachment; the PDF lived on Frame.io |
Domain reputation | msauth[.]biz was newly registered with 0/91 VirusTotal detections |
Sandboxing | A CAPTCHA blocked automated crawlers |
How Ocean caught it
Ray, Ocean’s central intelligence engine, retrieved the raw PDF through Frame.io’s API, inspected its /URI annotations, and found a redirect to a Cloudflare Pages subdomain. Ray followed every hop to the Microsoft 365 login clone and confirmed credential phishing before anyone entered a password.
What security teams should do
Block msauth[.]biz and its subdomains
Hunt for SaaS share notifications whose PDFs contain /URI annotations pointing off-platform, especially to new domains or *.pages.dev and *.workers.dev hosts
Inspect the shared asset itself; don’t rely on delivery signals or first-hop reputation for trusted SaaS shares
Indicators
Indicator | Priority |
|---|---|
msauth[.]biz | High |
office.msauth[.]biz | High |
/common/oauth2/v2.0/authorize path on msauth[.]biz | High |
167.99.178[.]222 | Medium |
pages.dev redirector | Medium |
notifications@frame[.]io | Provider infrastructure, do not block. |
Related reading
Ocean’s agents investigate every email for intent, including attacks no rule has been written for yet.